Tag: CISA KEV
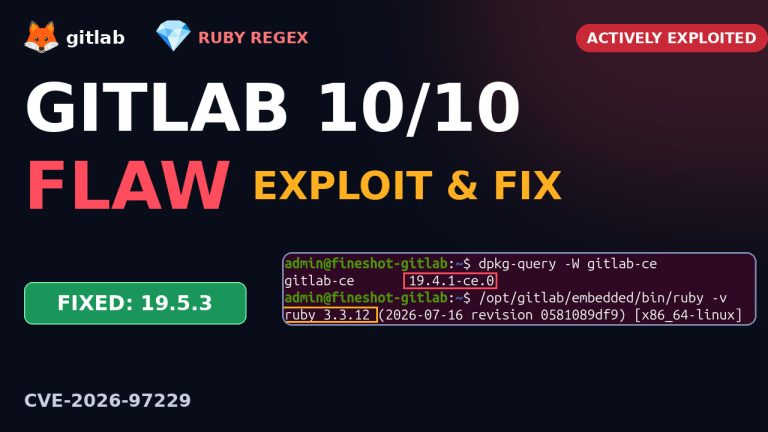
The GitLab 10/10 Flaw (CVE-2026-97229, GitLab2Shell): Why Updating GitLab Might Not Be Enough
One crafted regular expression in a CI/CD config can run code on a self-hosted GitLab server, no login needed. Alpine Linux updated and was still vulnerable. How to check, upgrade and verify.
Read more →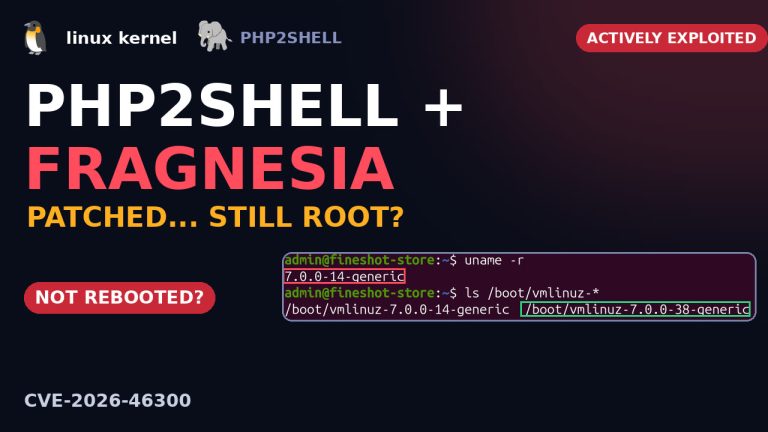
PHP2Shell + Fragnesia: Patched Linux Servers That Are Still Vulnerable to Root (CVE-2026-46300)
Attackers chain PHP2Shell (into your website) with Fragnesia (a Linux kernel bug) to get root. The kernel fix came out in May, yet servers still get hit, because the fix is installed but never running.
Read more →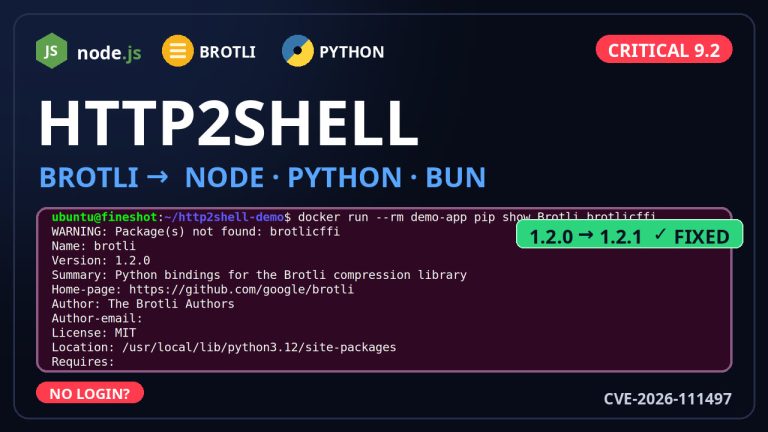
HTTP2Shell: How the Node.js Brotli Bug Spread to Python, Bun, Envoy and More
Node2Shell grew into HTTP2Shell: the same Brotli decoder bug (CVE-2026-111497) reaches Python HTTP clients, Bun, Envoy, Istio and curl. Who is exposed, how to check in one minute, and the fixed versions.
Read more →
Node2Shell Explained: The Node.js Brotli Bug (CVE-2026-111497) and How to Patch It
A critical bug in the Brotli decoder built into Node.js lets attackers corrupt server memory without logging in. What it is, who is affected, and a live patch on a real Ubuntu server.
Read more →